About LEONIS

Independent expertise.Practical impact.

LEONIS is an independent information security, risk, compliance and resilience advisory based in Sitges, Barcelona.

We help Spanish and European companies understand their obligations, manage the risks that matter and build practical programmes that protect the business — in Spain and wherever else they operate.

Our mission

To turn risk into resilience so organisations can thrive with confidence.

Independent advice, practical solutions and continuous support — tailored to your context and goals.

Who we are

Led by experience.Driven by purpose.

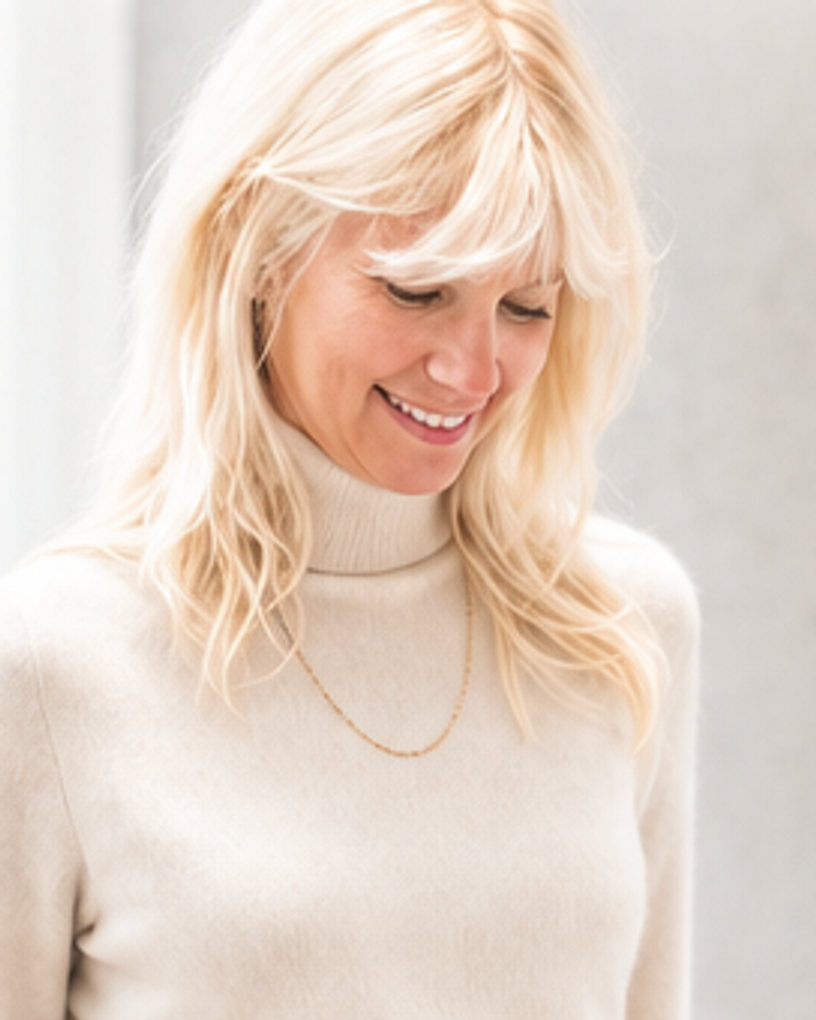
Portrait of Olha Mann, Founder and Principal Consultant of LEONIS

Olha Mann

Founder & Principal Consultant

Information security and risk management professional with 20+ years of international experience across manufacturing, technology, critical infrastructure and other industries.

Olha has built and audited management systems for organisations operating across multiple jurisdictions, advised executive teams on risk appetite and regulatory exposure, and led resilience programmes through real disruption — not just on paper.

Olha is the driving force behind LEONIS, shaping its direction and its commitment to independent advice, practical solutions and lasting resilience.

  • CISSP — Certified Information Systems Security Professional
  • CISM — Certified Information Security Manager
  • CEH — Certified Ethical Hacker
  • ISO/IEC 27001:2022 Lead Auditor
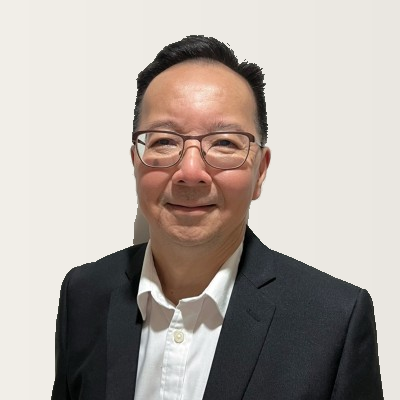
Portrait of Pete Siau, Principal Consultant at LEONIS

Pete Siau

Principal Consultant

Pete brings over 35 years of experience across IT infrastructure, operations, information security and governance, risk and compliance. His background spans oil and gas, telecommunications, manufacturing and financial services.

His expertise includes ISO 27001 ISMS and NIST CSF implementation, IT audits and requirements such as Sarbanes-Oxley, GDPR, SWIFT and China’s MLPS 2.0. Experience working with leadership teams across Asia-Pacific brings a regional perspective to clients with operations there.

  • CISM — Certified Information Security Manager
  • CISA — Certified Information Systems Auditor
  • ISO/IEC 27001 Lead Auditor
View Pete’s LinkedIn profile

How we work

Four commitments we hold ourselves to.

  1. Independence

    We sell no software and take no vendor commissions. Our recommendations answer only to your risk profile.

  2. Clarity

    Findings are written to be understood by the board and actioned by the team. No jargon for its own sake.

  3. Proportionality

    Controls are sized to your risk, your resources and your regulatory reality — never copied from a template.

  4. Continuity

    We stay engaged after the report. Resilience is a capability you build, not a document you file.

Not sure where to start?That’s fine.

You don’t need to know which regulation, standard or framework applies. Bring us your security, GDPR or compliance question, and we’ll help you agree practical next steps.

Let's talk